In development — waitlist open
Verifiable identity for AI agents
Sworncard is an issuer-side service, currently in development. Agent passports are designed to give a verifier evidence about who an agent is, what it may do, and who stands behind it — as signed credentials rather than a claim in a prompt.
Join the waitlist No product access yet — the waitlist is how we tell you when there is.
Our release axis
Three steps of increasing evidence. This is Sworncard's own release axis, not a rating defined by any standards body.
-
self-declared
The agent states its own attributes. Nothing is attested by a third party — useful for discovery, not for trust decisions.
-
attested
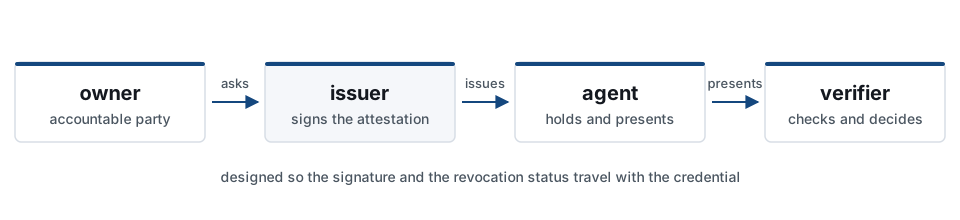
Sworncard is designed to issue credentials that bind an agent's stated capabilities to an attestation signed by us, and to publish their revocation status.
-
verified-owner Planned
Designed to add a verified identity for the party behind the agent, so a verifier can see who is accountable, not only what the agent claims.
Regulatory context
- Since Aug 2, 2026, EU AI Act Article 50 requires providers of AI systems intended to interact directly with people to ensure those people are informed they are interacting with AI (unless that is obvious from the context). Sworncard is designed to support that disclosure with verifiable evidence — a tool, not a compliance guarantee.
- Machine-readable marking of synthetic audio, image, video and text outputs: the transitional period ends Dec 2, 2026 for generative systems placed on the market before Aug 2, 2026.
- High-risk obligations for Annex III use-cases (Art. 6(2)) apply from Dec 2, 2027.
This page is not legal advice.
Standards
Designed for DIF KYA-OS: Protocol 1.0 (ratified July 2026); targeting the Entity Card 1.1 profile (current DIF TAAWG work item).
KYA-OS is the DIF work formerly known as MCP-I (ex-MCP-I).
Standards participation
Our proposals in the standard's tracker:
- kya-os-mcp proposal, issue 184
- kya-os-mcp proposal, issue 185
- kya-os-mcp proposal, issue 186
- kya-os-mcp proposal, issue 187
Proposals submitted for discussion in the working group.
Roadmap
- Planned Revocation kill-switch. Designed to withdraw an agent's standing across a delegation chain in one action.
- Planned Owner KYC levels (basic / enhanced / loa3). Designed to let a verifier see how strongly the party behind an agent was identified.
- Planned HTTP Message Signatures (RFC 9421) / Web Bot Auth compatibility. Designed so an agent's request can be checked by verifiers that already speak those protocols.
For people: Idemnia
Sworncard is for AI agents. For people there is Idemnia — personal identity cards.
Join the waitlist
We will send you a confirmation link. You are on the list once you open it.